Coinbase Vendor Breach Hits 70,000 Users
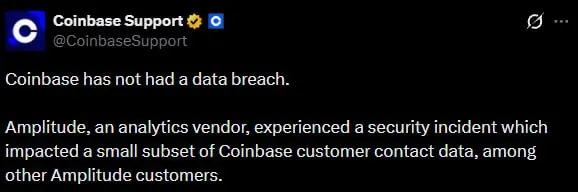
Coinbase confirmed that a third-party vendor suffered a security incident that exposed customer data for 70,000 users. The breach included confidential information tied to affected users’ Coinbase accounts, according to a statement posted on the platform’s official channel.
Scope of the Compromise
The vendor, whose identity Coinbase did not disclose, handled data that linked directly to user accounts on the exchange. While the exact nature of the stolen data remains unspecified, the announcement confirms that personal identifiers and account-related details were compromised.
Immediate Impact on Users
Users whose data was accessed may face increased risk of phishing or targeted scams. The breach does not indicate that account balances or transaction histories were exposed, but the presence of account-linked identifiers could enable attackers to craft convincing impersonation attempts.
Verification Steps for Affected Users
- Check account activity – Log into the Coinbase dashboard and review recent login events. Look for unfamiliar IP addresses or devices.
- Change passwords – Update the account password immediately, using a strong, unique combination that differs from other services.
- Enable two-factor authentication (2FA) – If not already active, set up 2FA via authenticator app or hardware token.
- Monitor email – Watch for suspicious emails that reference Coinbase or ask for account details.
- Report anomalies – Contact Coinbase support if you notice unauthorized activity.
Vendor Security Practices
The incident highlights the importance of vetting third-party vendors for data protection. Exchanges often outsource storage, analytics, or customer support to external firms. A breach in any of these partners can ripple back to the primary platform. Users should be aware that their data may travel through multiple channels before reaching the exchange’s servers.
Regulatory and Compliance Context
Regulators are increasingly scrutinizing how exchanges manage third-party risk. In the U.S., the Securities and Exchange Commission (SEC) and the Commodity Futures Trading Commission (CFTC) have issued guidance on vendor oversight. A breach of this scale could trigger investigations into Coinbase’s vendor management policies.
Market Reactions
Following the announcement, Coinbase’s share price dipped modestly in after-hours trading. The market reaction was muted compared to larger data-breach incidents, suggesting that investors view the incident as contained. Nonetheless, the event may influence future compliance costs for the exchange.
What to Watch Next
- Vendor disclosure – Coinbase may release more details about the vendor’s identity and the breach timeline.
- Security audit reports – Look for independent assessments of Coinbase’s third-party risk framework.
- Regulatory filings – Check for any SEC or CFTC filings that reference the incident.
Related Security Alerts
Readers who have followed recent wallet exploits may find parallels in the way attackers leverage compromised data. For example, the Bloom wallet exploit drains $947K from 49 wallets incident showed how stolen credentials can be used to drain funds.
Bottom Line
Coinbase’s confirmation of a third-party vendor breach affecting 70,000 customers serves as a reminder that data security extends beyond the primary exchange. Users should act promptly to secure their accounts and remain vigilant for phishing attempts that exploit the newly exposed information.
Related coverage
- GoDaddy SSL Revocation: 404,607 Certificates Pulled After Policy Errors
- Crypto.com Breach Fuels Targeted Scam Wave Against Top Holders
- Qubic Wallet Exploit Drains 1.4M From 1,400 Users