Bloom wallet exploit drains $947K from 49 wallets
Attackers Exploited a Third-Party Module
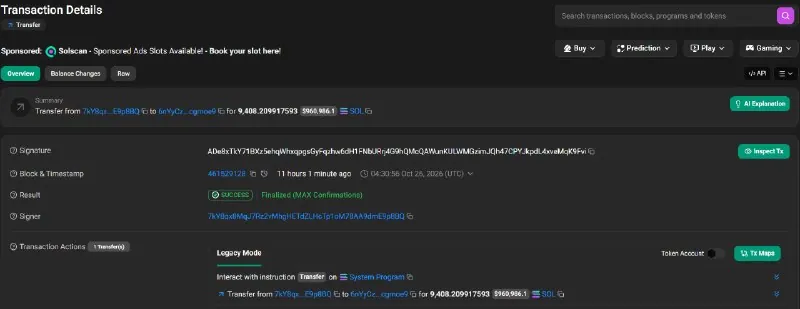
Bloom, a Solana-based wallet provider, announced that an attacker drained 9,408 SOL—worth roughly $947,000 at the time—from 49 wallets belonging to nine users. The theft occurred through a flaw in a third-party module integrated into Bloom’s infrastructure. The team emphasized that no private keys were compromised, and other wallets remain safe.
Bloom wallet exploit scope
The stolen amount aggregates to 9,408 SOL, distributed across 49 wallets. The incident involved nine distinct users, each with multiple wallets affected. Bloom’s public statement did not disclose individual wallet balances, but the total loss aligns with the transaction hash ADe8xTkY71BXz5ehqWhxqpgsGyFqzhw6dH1FNbURrj4G9hQMcQAWunKULWMGzimJQh47CPYJkpdL4xveMqK9Fvi, which can be examined on Solana explorers for verification.
Private keys remain secure
Bloom’s response clarified that the private keys associated with the affected wallets were not exposed. The breach stemmed from a logic error in the third-party module, not from key theft or phishing. Users who did not have their wallets drained can confirm that their private keys remain intact by checking the seed phrases or hardware wallet logs.
Reimbursement and tracing efforts
Bloom pledged full reimbursement to the affected users. The company is actively tracing the stolen funds, leveraging Solana’s transparent ledger to follow the transfer chain. While the exact recovery timeline is uncertain, Bloom’s commitment to reimbursement signals a proactive stance toward user trust.
What users should verify
- Check wallet balances – Compare current balances against pre-incident records.
- Inspect transaction history – Look for the transaction hash ADe8xTkY71BXz5ehqWhxqpgsGyFqzhw6dH1FNbURrj4G9hQMcQAWunKULWMGzimJQh47CPYJkpdL4xveMqK9Fvi on a Solana explorer.
- Confirm private key safety – Ensure seed phrases or hardware wallet logs show no unauthorized access.
- Monitor Bloom’s reimbursement updates – Follow official channels for status on fund recovery.
Broader implications for Solana wallets
The incident underscores the importance of vetting third-party modules. Even when private keys are secure, flawed logic can enable large-scale theft. Other Solana wallets may review dependency chains and implement stricter code reviews or formal verification where possible.
Related exploit cases
Bloom’s case joins a growing list of wallet exploits that have targeted Solana users. For example, the Qubic Wallet Exploit Drains 1.4M From 1,400 Users and the Initia MoveVM Exploit Halts Network After $2.7M Theft illustrate similar patterns of dependency-related vulnerabilities.
Sponsored
For live crypto prices, check the live crypto prices.
Next steps for users
- Audit your own wallet setup – Verify that all integrated modules are from trusted sources.
- Enable multi-factor authentication – Add an extra layer of security to wallet access.
- Stay informed – Follow Bloom’s updates and broader Solana security advisories.
The Bloom incident serves as a cautionary tale: secure keys do not guarantee immunity from theft if underlying code contains exploitable flaws. Vigilance in dependency management and prompt response to breaches remain critical for wallet providers and users alike.
Related coverage
- $2.7M Stolen, Then Lost in an Address-Poisoning Scam
- AI Wallet Attack: Bitcoin and Ether Holders Urged to Enter Bunker Mode
- Crypto.com Breach Fuels Targeted Scam Wave Against Top Holders