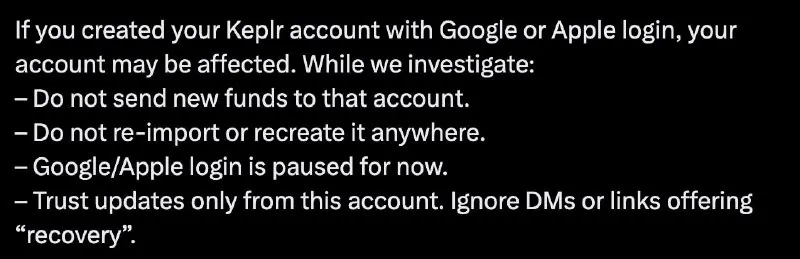
Keplr wallet users have reported a security breach that has drained over $6M from wallets whose seed phrases were stored via Gmail or Apple login. The exploit appears to target accounts that rely on email-based authentication, allowing attackers to access stored seed phrases and transfer funds.
The report, posted on a crypto forum, identifies the domain ownership of Keplr’s web interface as a potential vector for phishing. Users who logged in through Gmail or Apple are urged to verify that the domain they accessed matches the official Keplr domain and to check for any spoofed URLs that may have been used to harvest credentials.
Immediate protective action: move remaining assets to a new wallet where the seed phrase is stored offline, and enable two-factor authentication on all email accounts used for wallet recovery.
For context, a similar incident involving the Bloom wallet saw $947K drained from 49 wallets, highlighting the broader risk of email-based seed phrase storage. See the Bloom wallet exploit drains $947K from 49 wallets for details.
Related coverage
- Trust Wallet Exploit Targets iOS 18.5, $1.1M Stolen
- Wallet Owner Pleads for Return of $300K Stolen in Crypto Scam
- $2.7M Stolen, Then Lost in an Address-Poisoning Scam