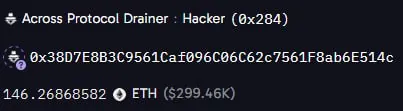
Across Protocol Site Compromised, Wallet Drainer Claims $300K Loss
A Telegram channel that tracks scams involving DWC users reported that a site belonging to Across Protocol was used to drain $300,000 from a victim’s wallet. The same domain was also visited by other users who reported similar losses. The incident appears to involve a phishing or wallet-draining exploit that targets users who interact with the site.
What the Evidence Shows
- A victim lost $300K in crypto assets after accessing the site.
- Other users have reported wallet drains after visiting the same domain.
- The pattern suggests a targeted phishing or wallet-draining attack.
How to Verify the Site’s Integrity
- Check WHOIS records for the domain to confirm the registered owner matches the legitimate Across Protocol entity.
- Inspect DNS records (A, AAAA, MX, TXT) for unexpected changes or hijacked entries.
- Compare SSL certificates against the official certificate issued by Across Protocol.
- Look for redirects to unfamiliar domains or IP addresses.
If any of these checks reveal discrepancies, treat the site as compromised.
Immediate Protective Action
- Disconnect any wallet that has interacted with the site.
- Notify your wallet provider and request a transaction review.
- Change passwords and enable two-factor authentication on all related accounts.
- Report the incident to relevant security forums and the platform’s support team.
Related coverage
- Domain and wallet-security source guide
- Keplr Wallet Exploit Claims $6M Stolen via Gmail and Apple Logins
- Wallet Owner Pleads for Return of $300K Stolen in Crypto Scam
Explore more on this topic
- More domains coverage