Initia MoveVM Exploit Halts Network After $2.7M Theft
On October 25, Initia halted its mainnet and rollup chains after a single transaction exposed a MoveVM vulnerability that allowed an attacker to mint new tokens and bridge out roughly $2.7M in AUSD, ETH and USDC. The incident was confirmed by the project’s co-founder, who noted that native INIT tokens remained safe.
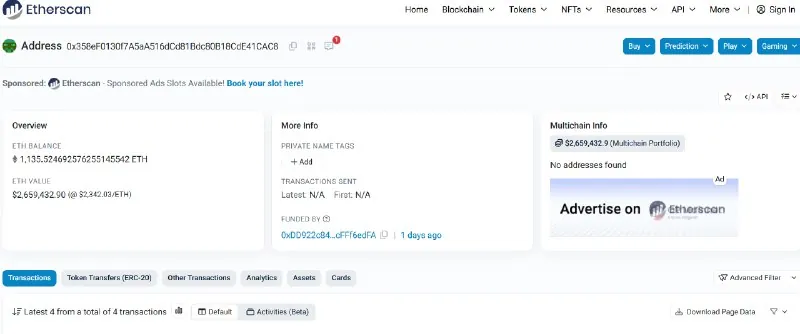
The exploit was executed via transaction 0x358eF0130f7A5aA516dCd81Bdc80B18CdE41CAC8, which leveraged a flaw in the MoveVM’s permission model. By crafting a malicious script, the attacker bypassed minting restrictions and routed the newly created assets through the bridge to external chains. The bridge operation completed before the network could detect the anomaly, resulting in the loss of the three supported stablecoins and a major Ethereum token.
Immediate Response and Network Status
Initia’s rapid shutdown prevented further outflows. The team paused all validator activity and rolled back the chain to a state before the exploit. Rollups were also halted to isolate the issue and prevent cross-chain amplification. The co-founder stated that the pause is temporary and will resume once a patch is deployed and the community is reassured.
Users who held AUSD, ETH or USDC on Initia should check the transaction hash on the official explorer. If the bridge output appears on a destination chain, the funds are likely irretrievable without a coordinated recovery effort from the bridge operator.
Technical Details of the MoveVM Flaw
MoveVM, the virtual machine that powers Initia’s smart contracts, enforces access control through a set of capabilities tied to account addresses. The flaw involved a missing check that allowed a contract to call the mint function without verifying the caller’s role. The attacker’s script executed the mint, then immediately invoked the bridge transfer, bypassing all subsequent validation layers.
Because the bridge contract trusts the source chain’s state, it accepted the forged mint as legitimate. The bridge then forwarded the assets to the specified destination addresses, completing the theft before any on-chain audit could flag the irregularity.
Market Impact and Investor Reaction
The $2.7M loss represents a significant portion of the liquidity pool for the affected assets on Initia. Market cap rankings for the platform’s native token, INIT, remain unchanged, but the incident may erode confidence among liquidity providers and traders.
Investors should monitor the project’s communication channels for updates on the patch timeline and any potential compensation mechanisms. The incident also highlights the importance of rigorous audit processes for MoveVM-based chains, especially those that support cross-chain bridges.
What Users Can Verify
- Transaction Hash – Use the explorer to confirm the status of 0x358eF0130f7A5aA516dCd81Bdc80B18CdE41CAC8.
- Bridge Records – Check the destination chain for any incoming transfers that match the amounts stolen.
- Token Balances – Verify that your INIT holdings are unchanged; the exploit did not affect the native token.
If any of these checks reveal discrepancies, report them to Initia’s support channels immediately.
Protective Action for Stakeholders
- Pause any pending cross-chain transfers until the network confirms a secure patch.
- Audit smart contracts that interact with Initia’s bridge to ensure they do not rely on unverified minting capabilities.
- Stay informed through official announcements; the project will publish a detailed technical report once the investigation concludes.
Sponsored
Related Exploit
The recent Qubic Wallet Exploit Drains 1.4M From 1,400 Users demonstrates a similar pattern of rapid asset drain via smart contract vulnerabilities. Comparing the two incidents may offer insights into common attack vectors across different blockchain ecosystems.
Related coverage
- X100 Protocol Exploit Seizes Senate Seats and Steals $4.85M
- Blockchain.com CFTC licenses: Pursuing Approval for Prediction Markets
- Crypto Scam Network Seized: FBI Shuts 112 Servers and 241 Sites