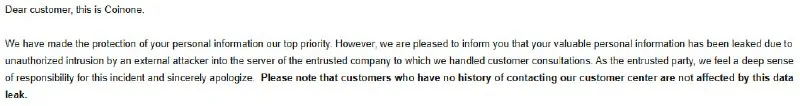
Coinone’s support desk was breached, exposing data for every user who contacted customer support. The attackers are now sending phishing emails, calls and texts to those users. Coinone has confirmed the incident and warned affected users to be vigilant.
The breach involved the support-desk infrastructure, not the exchange’s wallet system. Users who reached out to Coinone for help had their personal information leaked, creating a vector for targeted phishing.
Affected users should verify the domain of any email or message claiming to be from Coinone. The official support domain is listed on Coinone’s website; any deviation may indicate a spoofed sender. Contact Coinone directly through the verified channels to confirm any communication.
Related coverage
- [Domain and wallet-security source guide](/sources/
- SafePal Hardware Wallet Breach Sparks Phishing Calls
- Trust Wallet Exploit Targets iOS 18.5, $1.1M Stolen